
I have been working with Microsoft products and Windows for many years. Like many other users, I rely on Microsoft applications every day to manage files, emails and everyday tasks. Over the years, I have also noticed how much businesses depend on these tools. Outlook, OneDrive, Teams and SharePoint have become essential parts of daily business operations. But there is one important question that every business owner should ask: What happens if important data suddenly disappears?
A ransomware attack, an accidental deletion or a compromised user account can put years of business information at risk. Imagine losing important customer emails, financial documents or project files just when you need them most. The consequences can affect not only daily operations but also customer relationships and business continuity. One common misunderstanding is that Microsoft automatically protects all your data. However, this is only partly true. Microsoft is responsible for operating its services, but protecting your business data against accidental deletion, cyberattacks and other risks also requires additional measures.
In this article, I explain the most common causes of data loss in Microsoft 365 and show which protection measures really help. My goal is to help you understand the risks and make better decisions about protecting your business.
Why Data Loss in Microsoft 365 Happens More Often Than You Think
Many business owners believe that storing files in the cloud means they are automatically safe. After all, Microsoft 365 is a professional platform with built-in security and data protection features. But cloud storage does not mean that data can never be lost. In everyday business operations, employees create, edit, move and delete hundreds of files, emails and documents. They share folders with colleagues, change access permissions and work on documents from different devices. These activities are part of normal office work, but they can also lead to data loss.
The problem is that many incidents are not caused by a major technical failure. They start with a simple mistake, an incorrect setting or an account that has been accessed by someone who should not have access. Sometimes a company only notices the problem days or weeks later, when an important document is needed or a customer asks for an old email.
Microsoft provides features such as version history, recycle bins and retention policies. However, these features have limits and do not replace a complete backup strategy. If a company does not understand how its data is protected and how it can be recovered, even a small incident can become a serious business problem. Let’s look at the most common causes of data loss in Microsoft 365 and why they deserve attention.
1. Accidental Deletion by Employees
One of the most common causes of data loss is also one of the easiest to overlook: an employee deletes something by mistake.
Imagine an employee who wants to clean up an old project folder in SharePoint. The folder looks outdated, so they delete it without checking whether other departments still use the documents. A few days later, the sales team needs an important customer agreement from that folder. Nobody can find it.
Similar situations happen in Outlook and OneDrive. An employee may delete an email conversation that contains important customer agreements, payment details or project decisions. Someone may remove a shared document without realizing that several colleagues still depend on it. Another employee may overwrite an important file with an older version and save the changes.
These mistakes are part of normal business operations. Employees are often working under time pressure, handling several tasks at once or trying to keep their digital workspace organized. They do not always know which files are still important or who else depends on them.
The problem becomes more serious when nobody notices the deletion immediately. Microsoft 365 offers recovery options, such as recycle bins and version history, but these features do not keep every item forever. Recovery also depends on the type of data, the service involved and the available retention settings.
For business owners, this means that simply telling employees to be more careful is not enough. Companies need clear rules for handling important files and a reliable way to recover deleted or changed data. They should also know who is responsible for checking whether recovery is possible and how long deleted information remains available.
What businesses should do: Make sure employees understand how to handle shared files and important business documents. Check the recovery options in SharePoint, OneDrive and Exchange Online, and define how important data is backed up. Most importantly, test the recovery process instead of assuming that deleted files can always be restored.
2. Ransomware and Cyberattacks
Ransomware is one of the most serious threats to businesses today. Small and medium-sized companies are also attractive targets because attackers know that many of them have limited IT resources and may not have a clear recovery plan.
A ransomware attack often starts with something that looks harmless. An employee opens an email attachment, clicks on a link or downloads a file from an untrusted website. The malware then enters the company’s computer system and may spread to other connected devices and files.
Once the attackers gain access, they can encrypt important business data and demand money to restore access. This can affect customer records, financial documents, contracts and internal company files. In some cases, criminals also steal data before encrypting it. They may then threaten to publish sensitive information if the company refuses to pay.
Microsoft 365 does not automatically prevent this type of attack. OneDrive and SharePoint synchronize files between devices and the cloud. This is useful for everyday work, but it can also create problems during a ransomware incident. If malware encrypts files on an employee’s computer, the encrypted versions may be synchronized to OneDrive or SharePoint. As a result, damaged files can replace healthy versions in the cloud.
Microsoft 365 has version history and other recovery features that may help restore earlier versions. However, companies should not rely on these features as their only protection. The available recovery options depend on the situation, and attackers may also try to delete backups, change permissions or remove important data.
Email accounts are another common target. Attackers may steal login details through fake Microsoft 365 login pages. Once they gain access to an employee’s mailbox, they can read business conversations, search for invoices and payment information, or send convincing messages to customers and suppliers. They may even create forwarding rules to secretly receive copies of future emails.
For a small business, the consequences can be serious. Employees may be unable to work, customer orders may be delayed and important business information may become unavailable. Even after systems have been restored, the company may still face financial losses, legal questions and damage to its reputation.
What businesses should do: Keep computers and software up to date, use multi-factor authentication and protect Microsoft 365 accounts with appropriate security settings. Make sure important business data is backed up independently and that backups cannot easily be changed or deleted by attackers. Test the recovery process regularly so that your company knows how to restore its data after an incident.
3. Compromised User Accounts
A compromised user account is an account that has been accessed by someone who is not authorized to use it. This is particularly dangerous in Microsoft 365 because attackers can operate with the same permissions as the real employee.
Imagine that an employee receives an email that appears to come from Microsoft. The message says that their account needs attention and asks them to sign in. The employee clicks the link and enters their login details on a fake website. Within minutes, the attacker may have access to the account.
From that moment on, the attacker can potentially read emails, download documents, access shared files and send messages in the employee’s name. If the account has access to SharePoint sites, OneDrive folders or other company resources, the attacker may also be able to reach sensitive business information.
The situation can become particularly dangerous when the compromised account belongs to someone in management, finance or administration. For example, an attacker who gains access to the finance manager’s mailbox may study previous conversations with suppliers and learn how invoices are normally handled. They can then send a fake payment request that looks very convincing.
Attackers may also change mailbox settings, create automatic forwarding rules or add new ways to access an account. This allows them to monitor business communication without being noticed immediately. In some cases, they use the compromised account to send phishing emails to other employees, customers or business partners.
There are several ways in which login details can be stolen. Phishing emails are one common method. Passwords may also be exposed in data breaches involving other websites. If an employee uses the same password for several services, criminals may try those stolen details against the company’s Microsoft 365 accounts. Weak or easy-to-guess passwords create an additional risk.
The biggest problem is that a compromised account does not always cause an immediate warning. An attacker may simply read emails and collect information for days or weeks. By the time the company notices unusual activity, confidential information may already have been exposed or fraudulent messages may have been sent.
For business owners, this shows why account security is about more than choosing a strong password. Companies need to control who can access their systems, which information each account can reach and how unusual login activity is detected.
What businesses should do: Enable multi-factor authentication for all user accounts and use strong, unique passwords. Review access permissions regularly, especially for employees who handle financial or confidential information. Remove accounts that are no longer needed and make sure former employees cannot access company data. Microsoft 365 administrators should also monitor unusual sign-ins, suspicious mailbox rules and unexpected changes to account settings.
4. Incorrect Access Permissions
One important but often overlooked risk in Microsoft 365 is incorrect access management. Many companies give employees access to shared folders, documents and applications without regularly checking whether these permissions are still necessary.
Imagine that an employee from the sales department receives access to a SharePoint folder containing customer contracts and financial information. At first, this access may be needed for a specific project. However, nobody removes the permission when the project is finished. Months later, the employee can still open, download or change documents that are no longer relevant to their work.
The same problem can occur when files are shared with external people. An employee may send a SharePoint link to a supplier or business partner without checking whether the link allows access only to one person or to anyone who receives it. A confidential document can then be viewed or downloaded by people who were never supposed to see it.
Incorrect permissions can also lead to accidental changes or deletion. If too many employees have permission to edit important files, someone may overwrite a document, move it to another location or delete it without understanding the consequences. When several departments work with the same files, it can quickly become difficult to understand who changed something and why.
Another critical situation occurs when employees leave the company. Their Microsoft 365 accounts should be handled as part of the company’s employee departure process. If an account remains active or shared access is not reviewed, former employees may still be able to access company information. This is especially risky when employees leave on short notice or when nobody is clearly responsible for managing their accounts.
The problem is not limited to former employees. Temporary workers, external consultants and suppliers may also keep access to company resources long after their work has ended. Over time, these forgotten permissions create unnecessary security risks.
For business owners, this means that access rights should not be treated as a one-time setup. They need regular attention. Every employee should only have access to the information required for their job. This is known as the principle of least privilege, but the idea is simple: people should only be able to access what they actually need.
What businesses should do: Review user permissions in Microsoft 365 regularly, especially for SharePoint sites, OneDrive folders and shared documents. Remove access that is no longer required and use individual permissions instead of sharing sensitive information with large groups. Include Microsoft 365 account removal in the employee departure process. Also check external sharing settings and make sure confidential files are not accessible through unrestricted links.
5. Employee Mistakes and Lack of Knowledge
Employees are an important part of every company’s security. They work with emails, documents, customer information and shared files every day. However, they are not always aware of the risks involved in these activities. A lack of knowledge or unclear internal rules can lead to data loss, even when the company uses professional security tools.
Consider a typical situation: an employee receives an email that appears to come from a business partner. It contains a link to an important document and asks the employee to sign in. Without recognizing the warning signs, the employee enters their Microsoft 365 login details on a fake website. An attacker can then use the stolen information to access the company’s email account and files.
Other mistakes happen during normal office work. An employee saves important customer documents on their computer instead of in the company’s approved OneDrive or SharePoint location. If the device is damaged, stolen or infected with malware, these files may be lost. Another employee may store several versions of the same document in different folders. When a colleague needs the latest version, nobody knows which file is correct.
A lack of knowledge can also delay the response to an incident. For example, an employee notices that an important folder has disappeared or that unusual messages have been sent from their account. If they are unsure what to do, they may wait until someone else notices the problem. They might even try to fix it themselves and accidentally make the situation worse.
This is why employees need to know how to report suspicious activity and data loss. They should understand that reporting a mistake is not a reason to be blamed. The faster a company knows about a problem, the better its chances of limiting the damage and recovering the affected data.
Clear rules are just as important as security training. Employees should know where business documents must be stored, how files can be shared, which emails require special attention and who to contact when something goes wrong. These rules should be easy to understand and part of everyday work.
For business owners, the important point is that cybersecurity cannot be left entirely to technology. Even the best security settings cannot prevent every employee mistake. A company needs people who understand their responsibilities and know how to act when something unusual happens.
What businesses should do: Provide regular, practical cybersecurity training that uses examples from everyday office work. Explain how to recognize phishing emails, handle sensitive documents and use OneDrive and SharePoint correctly. Establish clear rules for storing and sharing company data. Make sure every employee knows who to contact when they notice suspicious activity, delete an important file or make a mistake. Most importantly, create an environment where employees feel comfortable reporting problems immediately.
Is Your Microsoft 365 Environment Really Secure?
Microsoft 365 is essential to your business. But are your data, user accounts and company information properly protected?
I help business owners understand their cybersecurity risks, identify security gaps and make informed decisions about protecting their IT environment. Take the next step towards better cybersecurity.
[Book Your Personal Cybersecurity Consultation]
The Most Important Protection Measures — and How They Work Together
Protecting your Microsoft 365 data does not have to be a large or expensive IT project. Many useful security features are already available in Microsoft 365, depending on your business license and configuration. Other protection measures, such as an independent backup solution, may require an additional service.
The important thing is to understand that no single security measure can protect your company against every type of data loss. Multi-factor authentication cannot prevent an employee from deleting the wrong folder. Version history cannot stop someone from stealing a password. And a backup is of little help if nobody checks whether the data can actually be restored.
That is why effective data protection needs several layers that work together. Each layer has a different purpose and protects your business against a different type of risk.
Layer 1: Protect User Accounts and Control Access
The first step is to make sure that only authorized people can access your company’s Microsoft 365 environment. If attackers cannot get into an account, they have a much harder time reaching emails, documents and other business information. Multi-factor authentication (MFA) adds an extra security step when someone signs in. Even if an attacker manages to steal an employee’s password, they may still be unable to access the account without the additional verification. Access permissions are equally important. Employees should only have access to the files and applications they need for their work. A member of the sales team, for example, may need customer documents but should not automatically have access to confidential HR records or financial information. These measures reduce the risk of unauthorized access and limit the damage if an account is compromised. They do not prevent every possible attack, but they make it much harder for criminals to move freely through company data.
Layer 2: Protect Files and Recover Everyday Changes
The second layer focuses on what happens to data during normal business operations. Employees create, edit, move and delete files every day. Even with good security rules, mistakes are unavoidable. Microsoft 365 offers several features that can help recover information after accidental changes or deletion. Version history allows users to access earlier versions of supported files. Recycle bins in services such as OneDrive and SharePoint can help restore deleted items. Retention policies can also help preserve certain information for a defined period, depending on how they are configured. These features are particularly useful when an employee accidentally deletes a document, overwrites an important file or removes information that is still needed by another department.
However, they have limits. Recovery options depend on the Microsoft 365 service, the type of data and the settings in place. Retention policies also serve specific purposes and should not automatically be treated as a complete backup solution. The key is to understand which recovery options are available in your company and how long important information remains recoverable.
Layer 3: Prepare for Serious Incidents with Independent Backups
The third layer protects your business when the built-in recovery options are not enough. This includes serious ransomware incidents, large-scale data deletion, compromised administrator accounts or situations where important information is discovered missing long after it was deleted. An independent backup solution creates additional copies of your Microsoft 365 data. Depending on the service and configuration, this may include emails, OneDrive files, SharePoint documents and other important business information.
The main advantage is that these backups are stored separately from the everyday Microsoft 365 environment. This can make it more difficult for an attacker who gains control of a company account to also delete or damage the backup copies. But simply having a backup is not enough. Your company needs to know how often backups are created, how long they are kept and who can access or delete them. Regular recovery tests are essential because they show whether the data can actually be restored when the business needs it. A backup that has never been tested is not a reliable recovery plan.
Multi-Factor Authentication: The Most Important First Step
A stolen password can be enough to give an attacker access to your company’s Microsoft 365 environment. This is one of the reasons why user accounts are such an attractive target. Criminals use different methods to obtain login details. They send fake Microsoft 365 emails, create websites that look like real login pages or use passwords exposed in data breaches. They may also try common passwords or reuse login details that employees use for several online services. The problem is that a password alone does not prove that the person signing in is really the account owner. If an attacker knows the correct password, they may be able to access emails, download business documents or use the account to send fraudulent messages. This is where Multi-Factor Authentication (MFA) makes an important difference.
MFA adds another security step to the login process. Instead of checking only the password, Microsoft 365 also asks the user to confirm their identity using a second factor. This is usually done through the Microsoft Authenticator app on a smartphone. The employee receives a sign-in request and must approve it or enter a number displayed during the login process. This means that knowing the password is no longer enough. An attacker would also need to complete the additional verification step. MFA therefore makes it much harder to take over an account, even when login details have been stolen.
For a small business, this is one of the most effective ways to improve account security without introducing complicated technology. Employees usually need to install the Authenticator app and register their account only once. After that, the additional confirmation takes just a few seconds when required. Depending on the company’s security settings, users may not need to confirm every single login on trusted devices.
Microsoft has reported that MFA can block more than 99.2% of account compromise attacks. This shows how important an additional verification step can be. However, MFA is not a complete guarantee. Attackers may still try to trick employees into approving fake login requests or use more advanced methods to bypass certain forms of verification. There are several points that businesses should consider when introducing MFA.
Protect administrator accounts first. Administrator accounts have extensive permissions in Microsoft 365. Anyone who gains access to such an account may be able to change security settings, manage users or access large amounts of company data. MFA should therefore be mandatory for every administrator account. Where possible, companies should also use separate administrator accounts for administrative tasks instead of using them for everyday email and office work.
Use modern authentication methods. Older login methods may not support modern security features such as MFA. These methods should be reviewed and disabled where they are no longer needed. Otherwise, older applications or services may create weaknesses that attackers can exploit. An IT service provider should check whether all applications and devices used by the company support the required authentication settings.
Teach employees to recognize unexpected login requests. An attacker who already knows an employee’s password may repeatedly send sign-in requests to the Authenticator app. This is sometimes called MFA fatigue. The attacker hopes that the employee will eventually approve a request simply to stop the notifications. Employees must understand that they should never approve a login they did not start themselves. If unexpected requests appear, they should report them to the IT administrator immediately.
Make sure there is a recovery process. What happens if an employee loses their smartphone, replaces their device or cannot access the Authenticator app? Companies should have a secure process for restoring access without simply removing the security protection. This is especially important for administrator accounts. For business owners, the key point is simple: MFA should not be optional for company accounts. It is a basic security measure that helps protect emails, files, customer information and other important business data.
What businesses should do: Ask your IT service provider whether MFA is enabled for every Microsoft 365 user account, including administrator accounts. Check which authentication methods are allowed and make sure older login methods are disabled where appropriate. Employees should also know how to report unexpected login requests and what to do if they lose access to their authentication device.
In this article, you will learn what MFA is, why it is important for small businesses, and how it helps protect against common cyber threats. We will also look at the well-known “99%” statistic, share best practices for implementing MFA, and highlight common mistakes that businesses should avoid.
Access Control: Give Everyone Only What They Need
Good access control follows a simple principle called “least privilege”: every person should have access only to the data and systems they actually need for their work. The marketing team does not need access to payroll documents, and a temporary project worker should not be able to open the complete customer database. Limiting access reduces the risk of accidental changes, unwanted data sharing and unauthorized access if an employee’s account is compromised.
In practice, this means organizing company data into clear areas with clearly defined permissions. In Microsoft 365, access can be managed through user groups, SharePoint sites and OneDrive sharing settings. Working with groups instead of assigning permissions to individual employees makes access easier to manage, especially when teams change or new employees join the company. Permissions should also be reviewed regularly, at least once or twice a year. Check whether employees still need their current access rights and whether external partners or temporary workers still require access to shared files. Pay particular attention to sensitive information, such as customer records, financial documents and employee data.
It is equally important to have a clear process when someone leaves the company. Their Microsoft 365 account should be disabled at the appropriate time, usually on their last working day. Access to shared resources should be removed, and important files, emails and business documents should be transferred to a manager or colleague where necessary. These steps do not require expensive additional software. They mainly require clear responsibilities, regular checks and a structured approach to managing user accounts. Done correctly, good access control can prevent many security problems before they happen.
What businesses should do: Ask your IT service provider to review Microsoft 365 access permissions. Make sure employees only have access to the information they need, external sharing is controlled and former employees cannot access company data.
Version History: Your Undo Button for Files
Version history is one of the most useful built-in features of Microsoft 365, yet many companies do not know how it works or how to use it. OneDrive and SharePoint can automatically keep previous versions of files whenever changes are made. This allows users to return to an earlier version if something goes wrong. Imagine that an employee is working on an important customer proposal. They make several changes and accidentally overwrite information that took hours to prepare. Instead of trying to recreate the missing content, they can open the file’s version history and restore an earlier version. The same feature can help when someone changes a shared document incorrectly or removes important information without noticing.
Version history can also be useful during certain ransomware incidents. If malware encrypts files on an employee’s computer and the changed files are synchronized with OneDrive or SharePoint, earlier versions may still be available. Users or administrators may then be able to restore a clean version of the affected document. However, this depends on the type of attack, the available versions and the recovery settings. Version history should never be treated as guaranteed protection against ransomware.
Business owners should make sure that version history is available for important files and that the retention settings meet the company’s needs. Microsoft 365 has default versioning settings, but the number of versions retained can depend on the service, storage location and configuration. Administrators should therefore check the actual settings instead of assuming that every file has the same protection. It is also important that employees know how to access version history and restore an earlier version. In many cases, they can do this directly from OneDrive or SharePoint without needing help from the IT department. For more serious incidents, an administrator may need to review the affected files and coordinate the recovery.
Version history is not a complete backup solution. It may not protect against every type of deletion, long-term data loss or an attacker who also gains control of the relevant accounts and recovery options. It is best understood as a fast and convenient way to undo unwanted changes to files.
What businesses should do: Ask your IT service provider to check the version history settings in OneDrive and SharePoint. Make sure important documents have suitable version retention and teach employees how to restore an earlier version. Also test the recovery process so that everyone knows what to do when a file is accidentally changed or deleted.
Secure Backups: The Independent Safety Net
This is the point where many business owners need to change their thinking. All the features mentioned so far — version history, retention policies, the recycle bin — are helpful, but they are all part of the same Microsoft system. If an attacker gains administrator access, if data is damaged in a way that also affects the built-in protection, or if the retention period has already ended, these features cannot save you. This is why many experts recommend a separate, independent backup solution for Microsoft 365. Such a solution copies your emails, files, Teams data and SharePoint content to a completely separate location, often in a different data center or even from a different provider. If the worst case happens, you can restore everything — complete mailboxes, whole folder structures, single files from a specific day. A separate backup also usually keeps data much longer than Microsoft’s built-in options, often for years.
In this guide, you’ll learn the best backup setup for small businesses in 2026, combining cloud, local and offline protection. You’ll see which tools are worth considering and how to build a strategy that keeps your business secure, compliant and running, whatever happens.
“Do we have backups?” For many organizations, this question effectively ends the cybersecurity discussion. Once the answer is “yes,” the topic is considered resolved. In reality, this assumption has become one of the most dangerous blind spots in modern IT environments. This article examines why backups fail in practice and what separates a backup that merely exists from one that actually protects the business.
Regular Recovery Tests: A Backup You Cannot Restore Is Worthless
Many companies have backups but have never tried to restore anything. This is a dangerous gap. A backup only has value if the recovery actually works — quickly and completely. Recovery tests should be done regularly, for example every three to six months. A test can be very simple: pick a random file from last month and restore it. Then try something bigger, like a complete mailbox. These tests answer the questions that really matter in an emergency: How long does a restore take? Who knows how to do it? Is the documentation up to date? A recovery test takes little time, but it turns a theoretical backup into real security. Business owners should make recovery tests a fixed item in their contract or service agreement with their IT provider.
When a ransomware attack strikes, many small business owners take a deep breath and tell themselves, “At least we have our cloud backups.” It is a comforting thought, but it can be a dangerous illusion. The painful reality is that ransomware can indeed encrypt cloud backups, and it happens more often than most people realize. Read here to find out what you can do in an emergency
Conclusion: How to Prevent Data Loss in Microsoft 365 — Simple Steps, Strong Protection
Microsoft 365 makes everyday business operations easier, but storing data in the cloud does not automatically protect it from loss. Accidental deletion, ransomware, compromised accounts and incorrect access permissions can all put important business information at risk. The right protection measures make a real difference. Multi-factor authentication, controlled access permissions, version history and independent backups help reduce these risks. But business owners also need to understand whether their current security measures are suitable and where weaknesses may exist.
You do not have to become an IT expert to protect your business. You need to understand the risks, ask the right questions and make informed decisions about your company’s security.
That’s where I come in. Through my cybersecurity consulting, I help business owners understand security risks, assess existing protection measures and identify practical ways to improve their company’s cybersecurity. Whether you want to learn more about Microsoft security solutions or need guidance on your company’s overall cybersecurity, the first step is understanding where you stand today.
I also recommend that you read the following articles
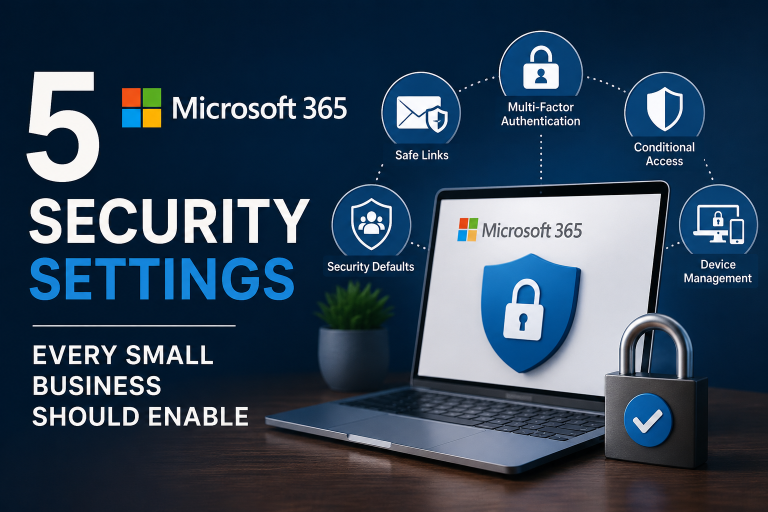
5 Microsoft 365 Security Settings Every Small Business Should Enable
How My Cybersecurity Mentoring Differs From Penetration Testing
How to create secure passwords that are extremely difficult to crack
How to Secure Microsoft 365: 7 Mistakes Small Businesses Make
What Happens When an Employee Leaves? The Microsoft 365 Security Checklist